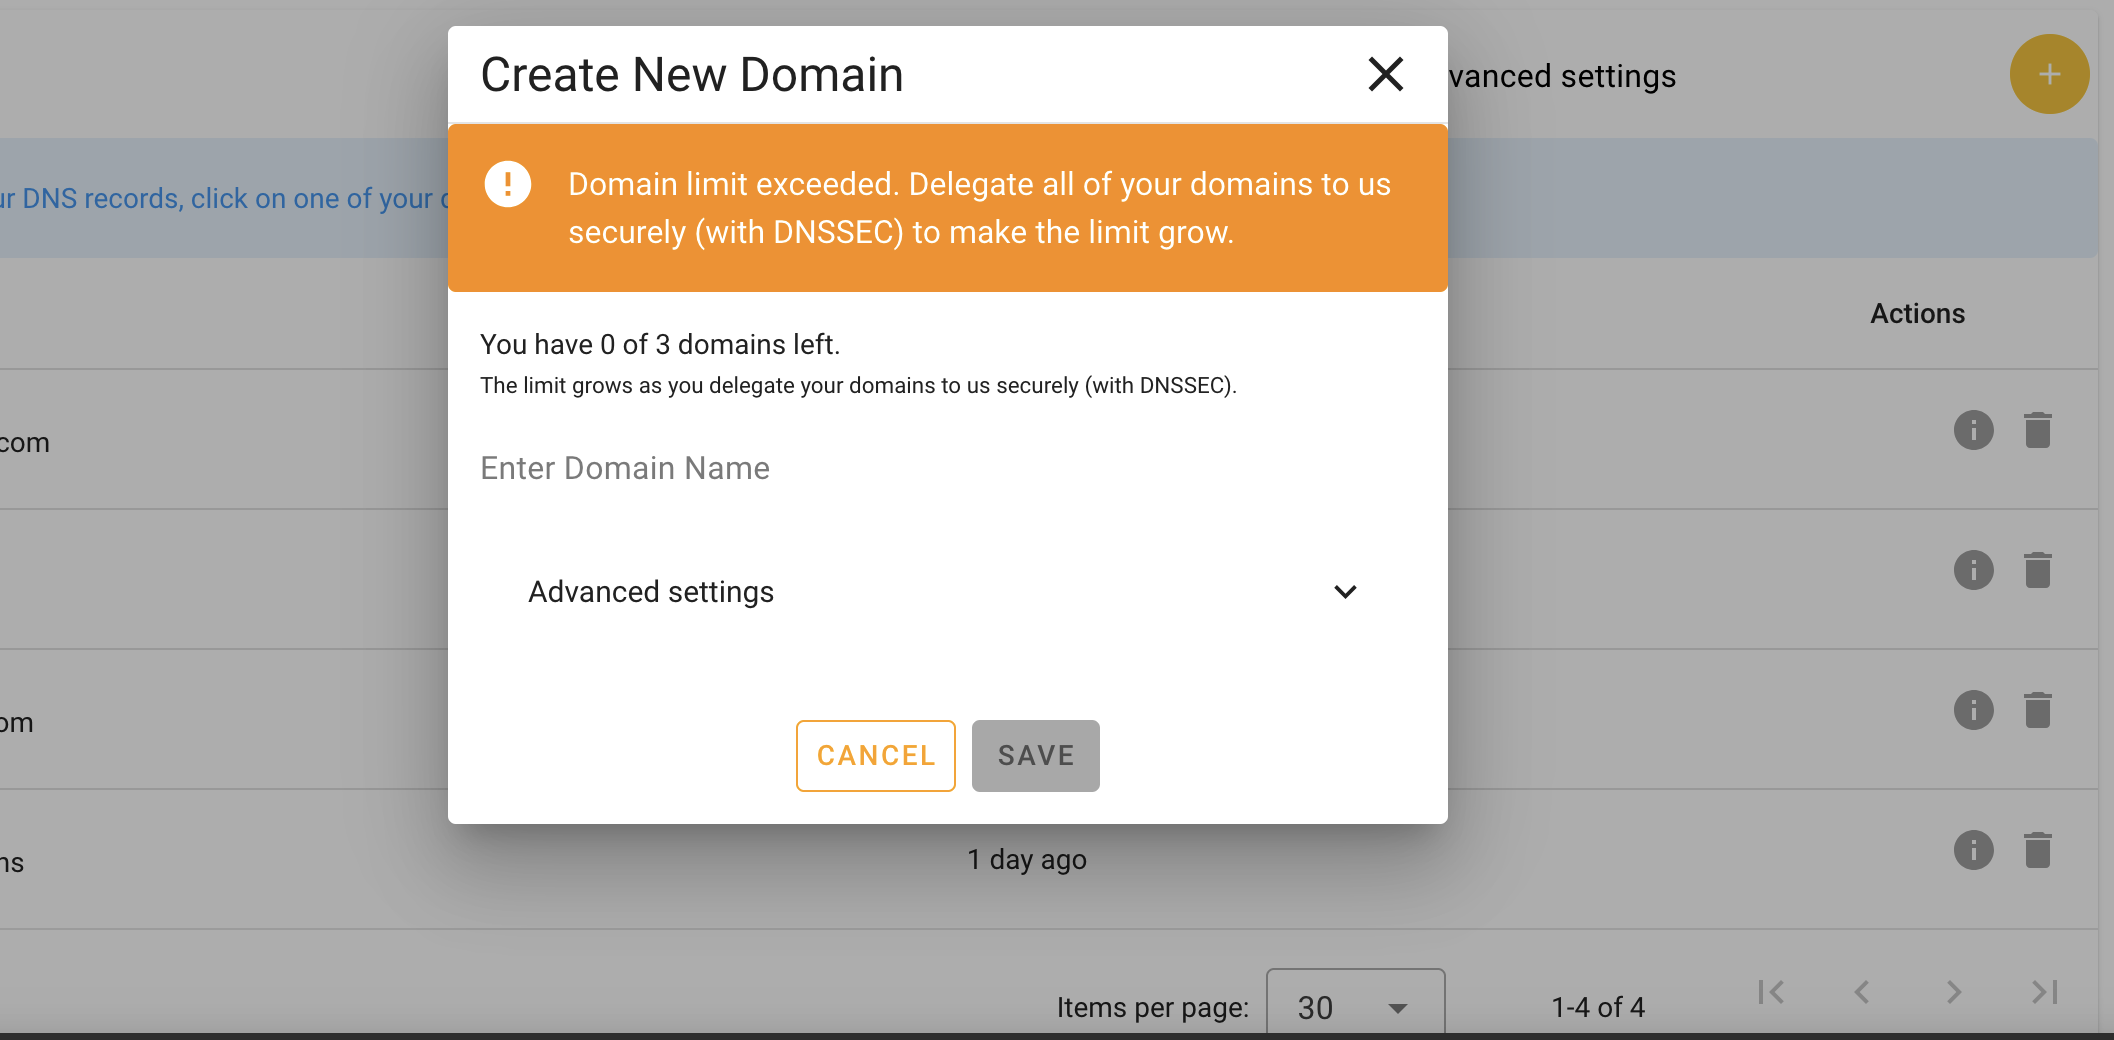
I’m a long time user and big fan of your services but I was really disappointed to learn about the recent changes on domain limits. I use desec with all of my domains and when I register new ones, the first thing is to set them up in desec.
You can probably imagine my surprise when I tried doing that today. I got one special domain in my portfolio that I have to check with the nic if the zone even support DNSSEC. I’m totally for DNSSEC and use it with all my other domains.
The thing I am disappointed about is the lack of communication. I had to find out about this change the hard way, when I needed to create a new zone. I could’ve reacted and contacted registry earlier if some kind of information was published. I mean you got the users email address, this would’ve been a good opportunity to use it. I really hope you could inform the users about such grand changes more reliably in the future.
Thanks again for your great service. I’m now in touch with the registrar and if it can’t be resolved on their end I hope I can shoot you a mail to further discuss this.
The deSEC project is all about increasing security on the internet, promoting secure DNS delegations by enabling DNSSEC. Their ToS state that secure delegation is required. For each domain that is securely delegated, your limit grows, so if you use deSEC as intended, you should not encounter any issues with limits.
To be fair, IMHO the current tester is broken. I havn’t really bothered, since I currently don’t want to add a domain. But I have 4 domains, all with working DNSSEC and I still get this:
As I stated before i got one domain, which is such a special zone that I need to check if they even support DNSSEC, which leaves me in a situation that I got 5 domain, 4 are secured and 1 isn’t. And I’m just saying that it would’ve been great to be informed before these changes apply.
When I started using desec I personally requested a higher domain count for my account via mail, so ofc I’m surprised that this was changed without notice.
I noticed that I now find myself in a situation that I can’t get out of without removing one domain if DNSSEC isn’t possible for the ones that are allowed to not have DNSSEC enabled.
I have also asked the support some time ago to increase the limit, they also changed it to 15.
However, i found out that if your limits are stuck, you can trigger a re-check if you try to add a new domain to your account. The API will return a answer saying that you reached your limits, but at the same time it will trigger a re-check to check if your domains are DNSSEC protected.
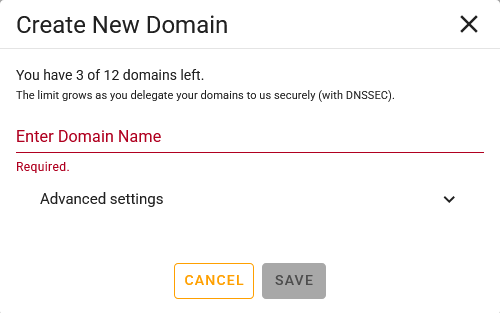
If you are on the “new limits” it should look like this and it should automatically increase, but like i said you can try to trigger a re-check if u try to add a domain via the API.
curl ``https://desec.io/api/v1/domains/`` --header "Authorization: Token 7VrVn8v4hpf89DAfd6q4MjE8UUZo" --header "Content-Type: application/json" --data @- <<< '{"name": "``architekt-talk.com``"}' {"detail":"Domain limit exceeded. The limit grows as you delegate your domains to us securely (with DNSSEC); we are re-checking yours now."}%
don’t worry, token is no longer valid.
Also funny that I have 4 domains running but the webGUI tells me that I have 0 left out of 4
Hmmmm, very weird. I sadly can’t try it right now because i do not have any more domains to add at this point. But it worked for me last week and i also had to read about the “new limits”. I migrated one domain after another, then hit the limit, re-checked a few times and then i was able to grow the limit and add the remaining domains.
Thank you for sharing your feedback on our new dynamic limits. Also, @CId38luYWOO4W1 and @Yuna, welcome to deSEC!
We make a point of not sending too much mail to our users. In this case, we did inform those who had an immediate need for action, in particular when a significant limit increase (> 15) had previously been granted and the dynamic limit now
was exceeded due to unused domains (delete to get back on track);
was exceeded due to domains without DNSSEC (enable to get back on track);
was exactly reached due to domains without DNSSEC (enable to allow creating more);
was not reached, but there was a significant fraction of incorrectly configured domains.
We did not inform everyone whom we had granted our standard limit bump to 15, as in the process of increasing limits we had required users to signal their willingness to enable DNSSEC – so we didn’t feel like we’re violating any agreement for those who did not, and considered the explanation now shown in the “Create Domain” dialog to be a sufficient reminder.
This allowed us to send only a few hundred emails, instead of tens of thousands. As our terms always required enabling DNSSEC and the rules didn’t actually change, we figured that this was acceptable. Apologies if it wasn’t what everyone expected!
Exactly.
You may be wrong Please reach out to support if you’d like us to look into your account.
For now (without a guarantee for the future), the limit is max(1, s + round(sqrt(s))), were s is the number of domains delegated to us with DNSSEC enabled. Thus, if like in your case, s = 4, your limit is 6, and you can enable one more domain if you currently have 5 (as you say).
This mechanism enforces DNSSEC individually for the first few domains, and when you’ve built a track record (after the third one), the headroom increases more and more, so you can create more domains without waiting separately for each one’s DNSSEC status to be detected.
(Note that asymptotically the relative fraction of non-DNSSEC domains still goes down as 1/sqrt(s).)
That’s correct; a POST request to the domains/ endpoint triggers a recheck when the limit has been reached.
This is currently not easily accessible in the web interface. We’re planning to add a recheck button later this month, and will also provide visibility into each domain’s status.