Hi all, I just wonder how long it takes for the automatic domain limit increase. Should it be instantaneous? Or the day(s) after? I’ve created my first domain and secured it with DNSSEC and dig says that it was successful. What have been your experiences?
Hi! Me too! I added a zone with DNSSEC on my account and waited and no increase.
Took me a day on my domain. even while the famous online checkers confirm, the caching DNS deSEC uses needs to timeout its current values…
My AI gave me this summary after review of the desec github repo:
1. Immediate trigger: As soon as you hit the limit, the API schedules an ad-hoc check (enqueue_user_delegation_check, api/desecapi/tasks.py) – max. once per minute per user, up to 20 domains per run, least-recently-checked first.
2. The check itself: Each domain check typically takes < 2 s (max ~30 s, hard cap 300 s). The worker processes ad-hoc jobs round-robin, so you wait at most one check, not a whole sweep.
3. The limit grows immediately once a check returns SECURE + CORRECTLY_DELEGATED – there is no waiting/hysteresis period.
The real bottleneck is DNS, not desec: The check must be able to see the DS/DNSSEC chain via the parent zone. If you just switched DNSSEC on, the DS record at your registrar must first be published/propagated (DS TTLs: minutes to hours, worst case 1–2 days).
Here it took more or less exactly 24h.
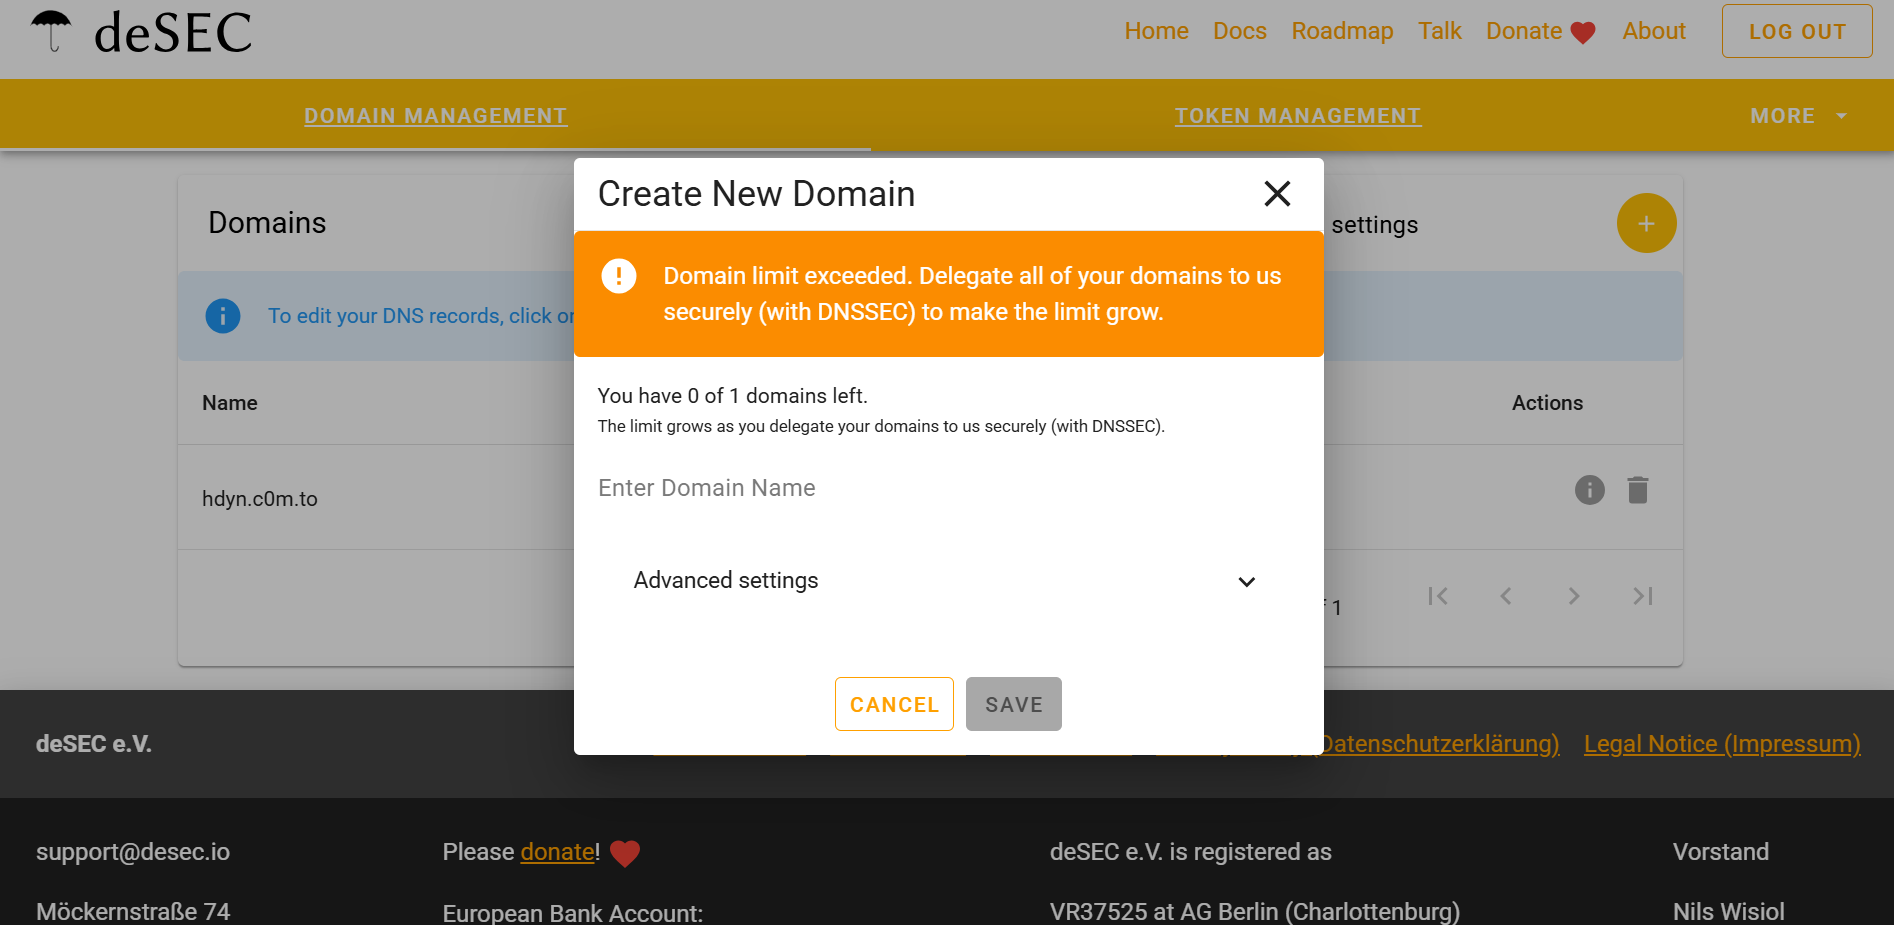
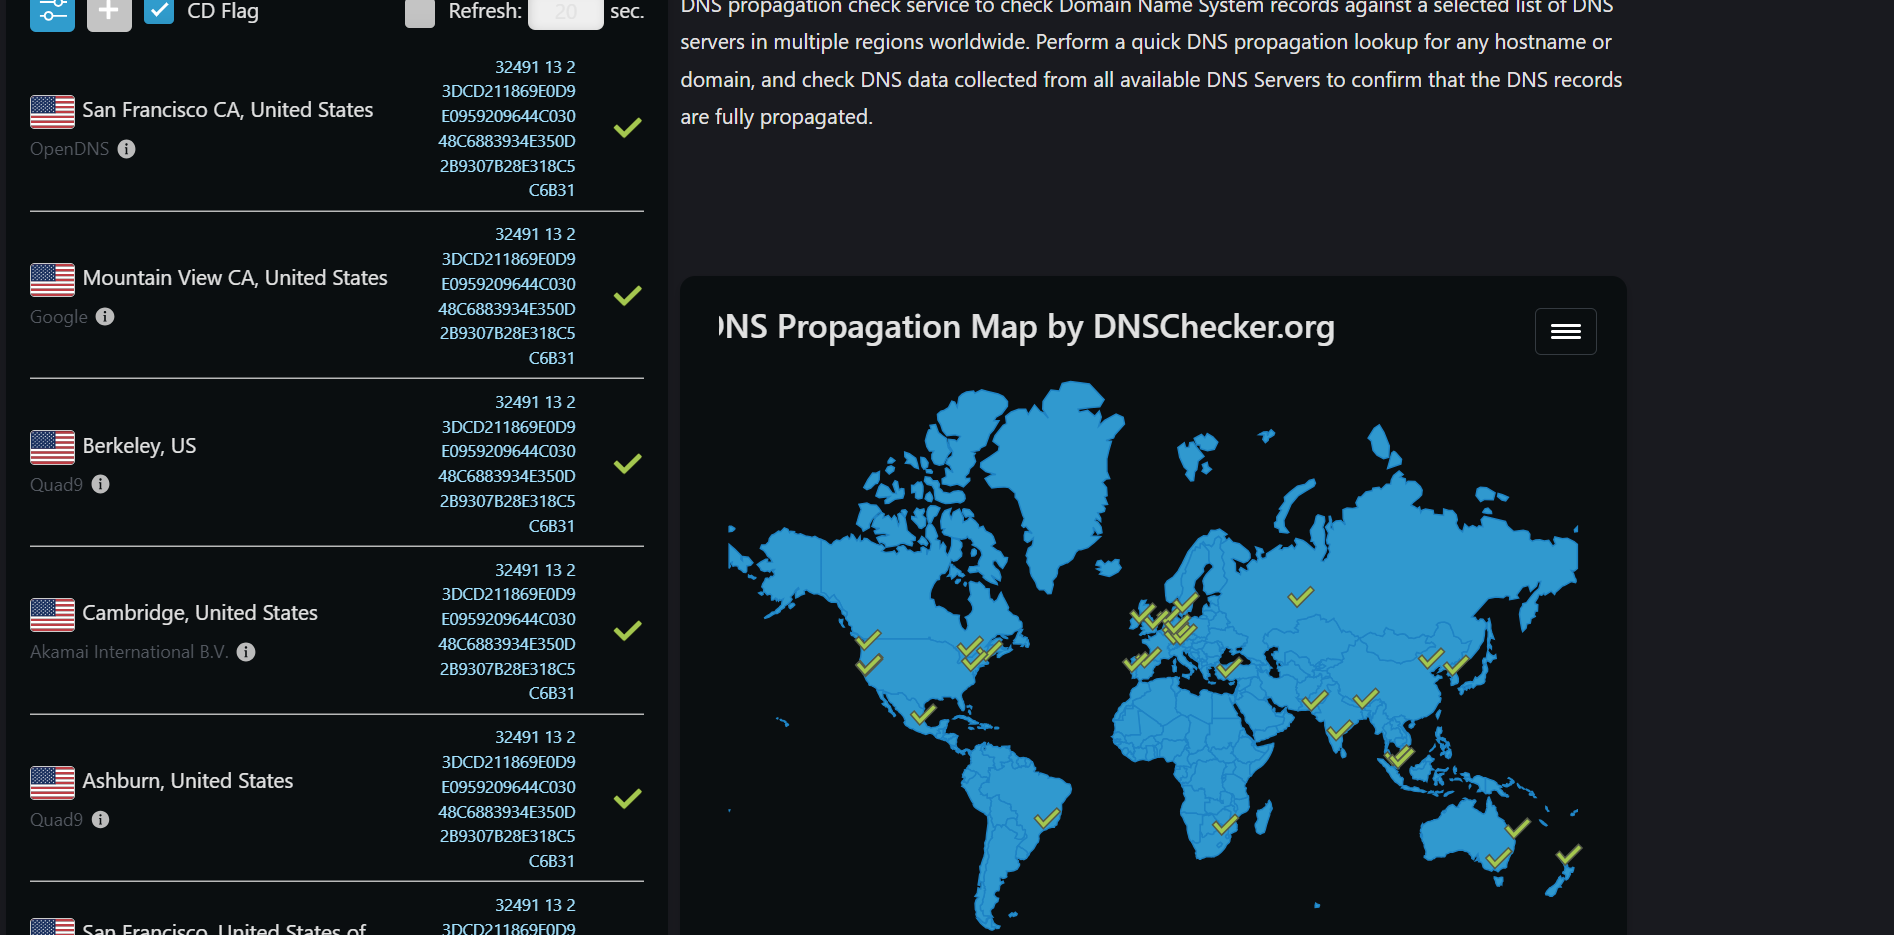
check again couple of minutes later. each time you try to add a domain and you get that limitation error, the api is running a verification in of minutes. it might become ratelimited though according to sourcecode
Is it possible that this immediate validation is triggered only when using the API (and not the web interface)?
Hi! I did use the rrset api to add a new rrset to my zone but stil nothing
you can trigger the re–check if u try to add a new domain via the API, yes.
Yes, my point was: You should try to add a new domain via the API. Trying to add it via the Web interface does not trigger the re-check. (But that’s just my guess.)
Hi! I did try this but got this:
{“detail”:“Domain limit exceeded. The limit grows as you delegate your domains to us securely
(with DNSSEC); we are re-checking yours now.”}
After that try again after a few seconds. If all domains are correctly delegated the limit will grow.
But I still find it very awkward that the limit was introduced without any way to see which domain is flagged. No info, nothing. Just in the API is a value with how many domains are secured but not which ones.
Hi @gsaelzbrot,
Thanks for your message, and welcome to deSEC! 
Our checker normally runs after a few hours (max 1 day) for each account (but see below).
DNS caching is not relevant as we always fetch fresh DNSSEC information.
That’s correct; a POST request to the domains/ endpoint triggers a recheck when the limit has been reached.
This is currently not easily accessible in the web interface. We’re planning to add a recheck button later this month, and will also provide visibility into each domain’s status.
We’re collecting more feedback on this here: Feedback about recent limit changes
Stay secure,
Peter